Resources
Security and data

Controls, not slogans.

Public safety software holds personnel files, staffing decisions, client billing, and the records a grievance turns on. One Bridge Tec is built so the agency decides who sees what, every action that matters is logged, and data stays in the jurisdiction the agency chooses — and we describe exactly what we do rather than what we wish we could claim.

In a police headquarters corridor, an IT security manager holds his badge to a card reader beside a server-room door while a uniformed inspector with a folder watches.
Role-basedaccess configured by the agency — operational, personnel, and financial data stay with the people who need them
Loggedoffers, changes, approvals, record edits, and permission changes, with who and when
Your jurisdictionhosting location and residency chosen by the agency and written into the contract
On-site AIPrivate AI runs inside the agency — no protected data sent to a third-party AI service
What procurement asks

Four questions every security review comes down to

Access

Who can see this?

Personnel files, staffing decisions, and billing are each sensitive to different people. The answer has to be specific to a role, and the agency has to be the one who sets it.
Accountability

What happened, and who did it?

The moment a decision is challenged, the record has to already exist. Rebuilding it from inboxes is how agencies lose grievances they were right about.

Residency

Where does the data live?

Records, privacy, and legal want a location and a contract clause, not a preference. The answer has to be the agency's choice and written down.

Honesty

What do you actually certify?

A vendor's badges are only worth what they have been audited against. If it is not held, it should not be on the page.

The controls

Access, audit, and where the data lives

The three controls that carry a public-safety security review, and how each works across 1 Bridge Tec HRIS, One Bridge 10-8, and Private AI, because they share one foundation.
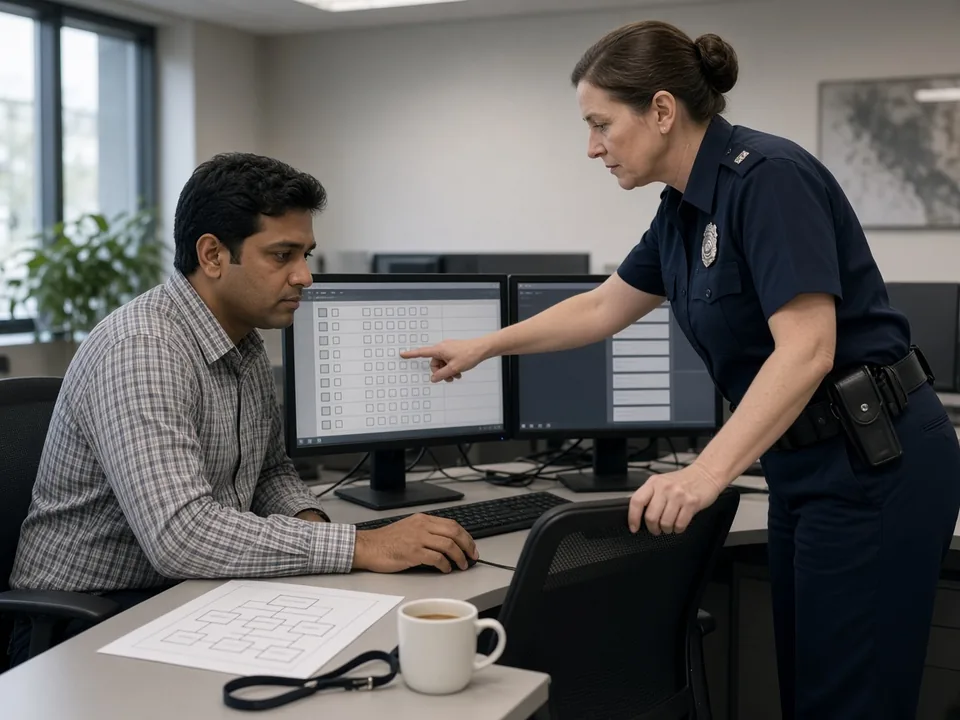
A civilian systems administrator and a uniformed staff sergeant review a role-permissions matrix on two monitors in a police headquarters office
Access

Who sees what is decided by the agency, role by role

A paid-duty coordinator does not need a member's medical leave. A sergeant does not need the client's rate card. Permissions in every One Bridge Tec product are role-based and configured by the agency during implementation, so operational, personnel, and financial data stay with the people whose job requires them.
  • Roles map to how your service is actually organized: rank, unit, function
  • Members see their own record and offers; clients see their own requests
  • Access changes are themselves logged, with who made them and when
How roles are configured
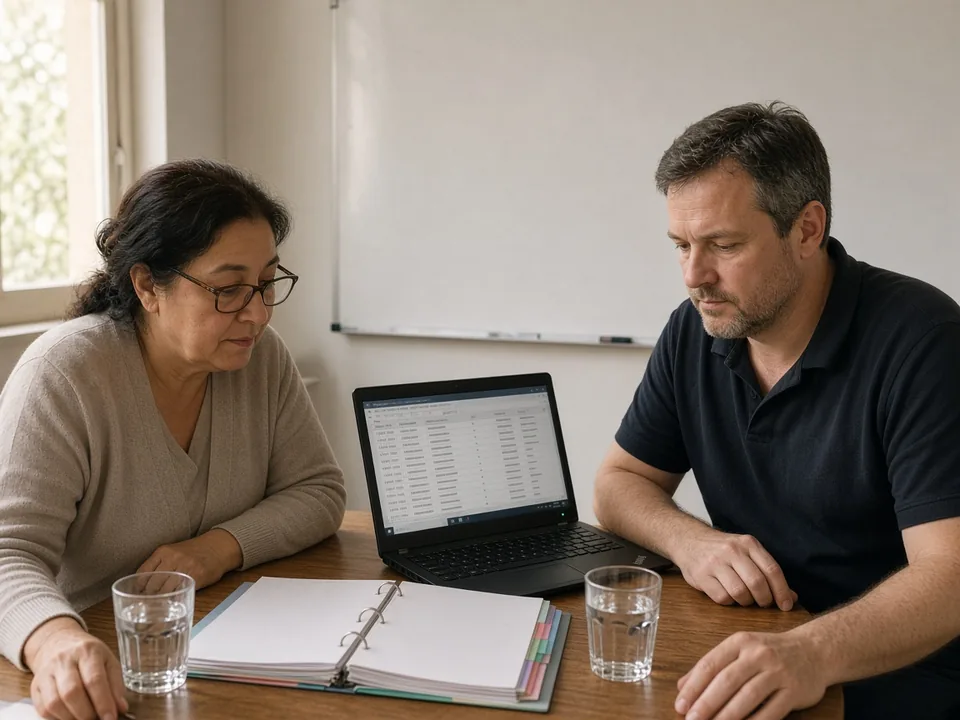
A professional-standards analyst and an association representative review a chronological event log on a laptop beside an open tabbed binder
Audit

Every offer, change, and approval, with who and when

When a grievance, a client dispute, or an access review asks what happened, the answer should be a record, not a reconstruction from email. One Bridge Tec products log the actions that matter — offers and responses, assignment changes, approvals, record edits, and permission changes — in a trail the right people can read.
  • Actions logged as they happen, not summarized after
  • Readable by the roles the agency authorizes, including association review where agreed
  • The same log the coordinator, the chief, and finance are looking at
What leaders see
A modern secured server room in a police headquarters with tidy enterprise racks and a glass door with a badge reader
Where data lives

Your data stays in the jurisdiction you choose

Where agency data is hosted is a decision the agency makes and we honour: infrastructure in your jurisdiction, a facility your service controls, or hardware inside your own building. With Private AI, the models that read your records run on-site, so no protected data is sent to a third-party AI service. Residency, backup, and retention terms are written into each engagement, not implied by a slogan.

  • Hosting location and residency confirmed in the contract for each agency
  • Private AI runs on hardware installed at the agency — nothing leaves for a third-party AI service
  • Backup and retention arrangements scoped with your records and privacy officers
How Private AI keeps data inside
What we do not claim

Honest boundaries

A security page is only useful if you can rely on what it leaves out. We do not invent certifications, promise absolute security, or imply residency terms that are not yet contracted for your deployment.

Certifications

Listed only when held

If a certification or attestation is not named on this page, we do not hold it and we do not imply it. When we obtain one, it will be listed with its scope and date.

Residency

Confirmed per engagement

Hosting location, residency, backup, and retention are scoped with each agency and written into the agreement. We do not make a blanket promise that a contract has not yet made.

Guarantees

Practices, not absolutes

We describe how access, logging, encryption, and deployment work. We do not use the words 'unhackable', 'military-grade', or 'guaranteed', because no honest vendor can.

Disclosure

A way to tell us when we are wrong

Security researchers and agency staff can report a vulnerability through our responsible-disclosure process, and we commit to acknowledging and acting on it.

AI without the data leak

The AI reads your records inside your building, and nowhere else

Most AI features send agency text to a vendor's cloud. Private AI runs open-weight models on hardware installed at the agency, grounded only in the sources you approve, so the security review of the AI is the same review as the rest of the system.

Boundary

No protected data to third-party AI services

Prompts, records, and answers stay on agency hardware. There is no vendor API in the path for a personnel file or a staffing decision to leak through.

Grounding

Answers cite your sources

The AI answers from your policies, agreements, and records, with citations, so an answer can be checked against the document it came from.

Accountability

People decide; the log shows it

The AI drafts, scores, and explains. Hiring, staffing, and discipline decisions are made by people, and those decisions are logged like every other action.

Security review

Send us the questionnaire.

Bring your records officer, your privacy officer, and your IT lead. We will walk through roles, the audit trail, hosting options for your jurisdiction, and how Private AI is contained — and we will answer your procurement questionnaire in writing, including the questions where the honest answer is "not yet."

Procurement FAQ

Questions security reviews ask

Where will the system be hosted?
Where the agency decides. Options include infrastructure in your jurisdiction, a facility your service controls, or hardware installed in your own building. Exact hosting, residency, backup, and retention arrangements are confirmed in writing for each engagement.
Who can access operational, personnel, and financial data?
Access is role-based and configured by the agency. You decide which administrators, supervisors, leaders, members, and clients can see which records, and changes to those permissions are logged.
What is logged, and who can read the log?
Offers and responses, assignment changes, approvals, record edits, and permission changes are logged with who acted and when. The agency decides which roles can read the log, and can extend read access to association review where your agreement provides for it.
Is data encrypted?
Data is encrypted in transit and at rest. Key management and any additional controls your jurisdiction requires are confirmed as part of the deployment scope.
Does the AI send our data to an outside service?
No. Private AI runs on hardware installed at the agency. Prompts, records, and answers stay on that hardware, and no protected data is sent to a third-party AI service. If an agency chooses to use a third-party API instead, that is an explicit decision the agency makes, not a default.
Do you claim specific compliance certifications?
Only certifications and attestations One Bridge Tec currently holds are listed on this page. If it is not listed, we do not hold it and we will tell you so directly in your questionnaire.
How are website demo requests handled?
Demo requests submitted through this site are used only to respond and schedule a conversation, and are not sold or shared for marketing. See the Privacy Policy for details.

Ask the hard questions. We will answer them in writing.

Roles, audit trail, hosting for your jurisdiction, and how the AI is contained, with your records, privacy, and IT leads in the room.